Basic Active directory configuration example
VKB-1166Reference
- 📦 Applies to
- Xen Orchestra
- 🗓️ Created
- 2025-07-17
- 🔄 Updated
- 2025-07-17
- 🏷️ Tags
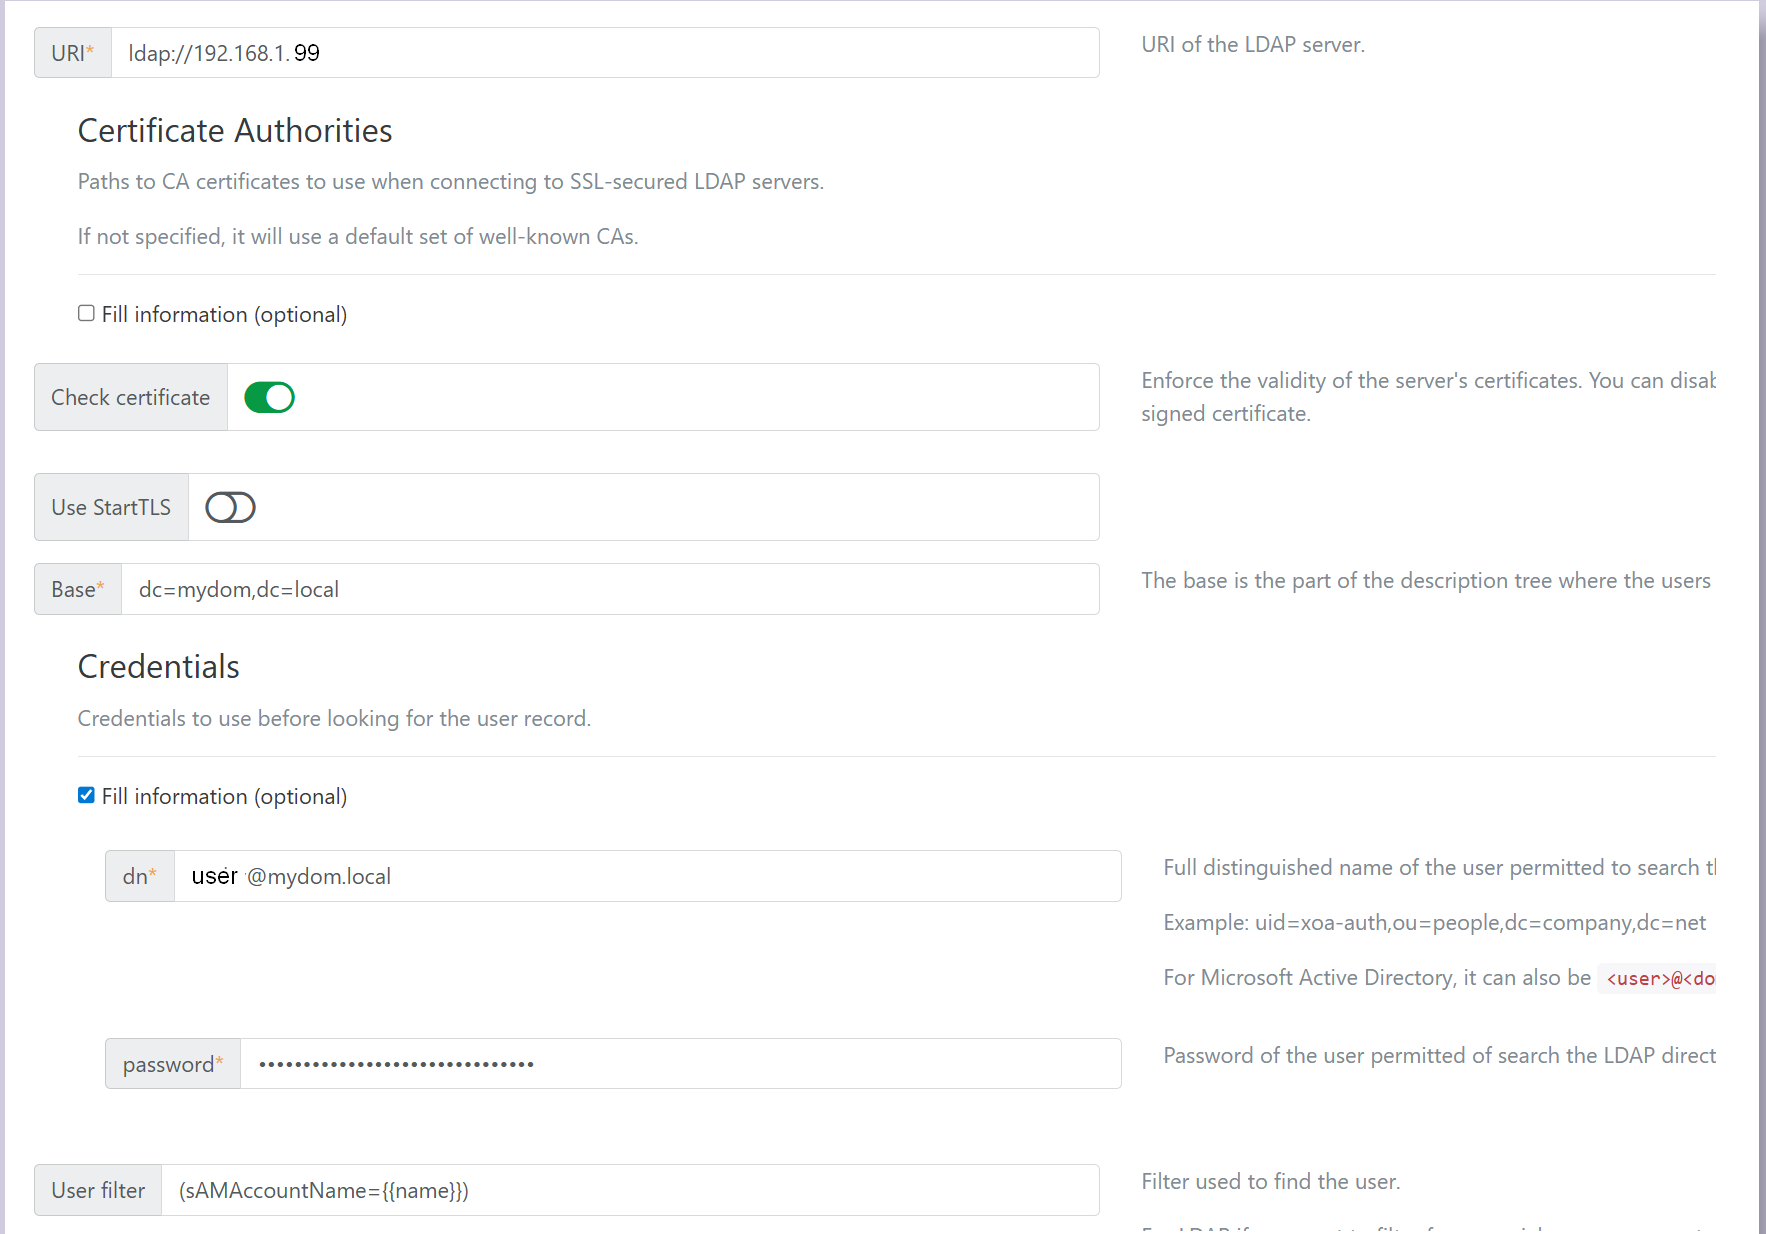
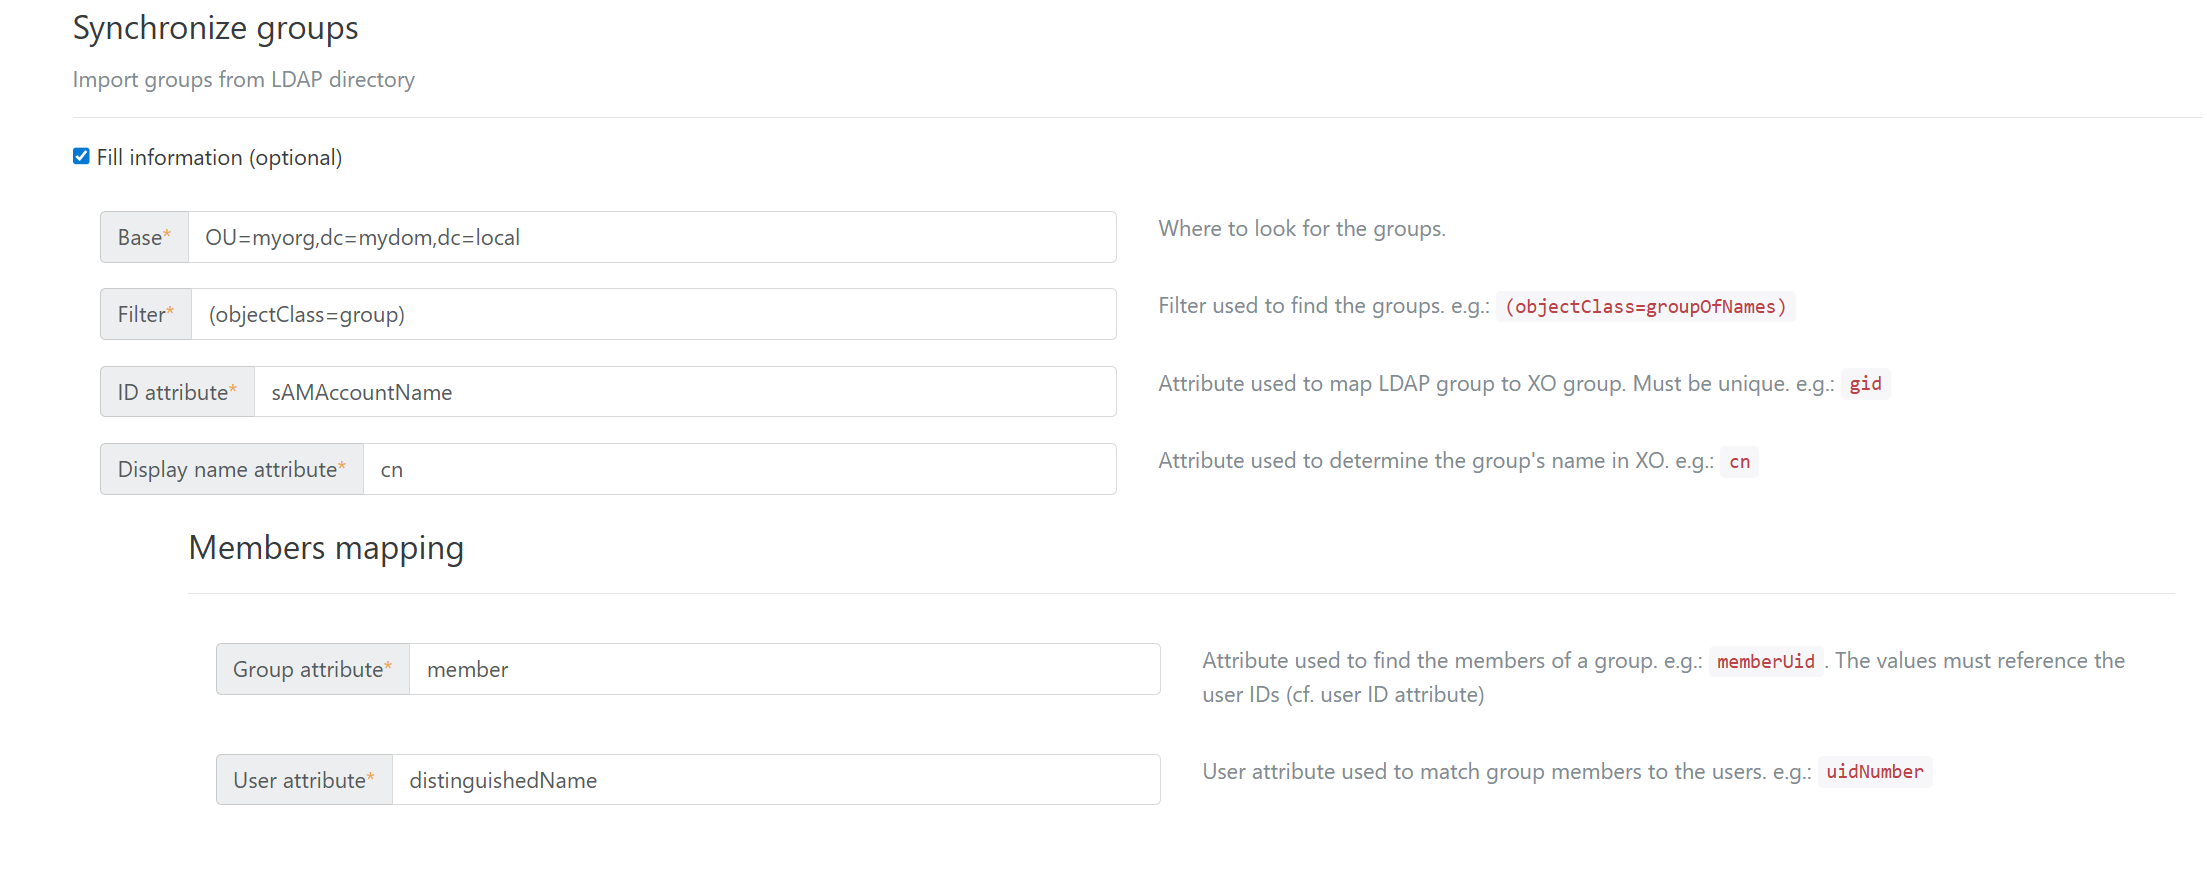
Field-by-field example:
- URL: should be filled with the AD URL. Example:
ldap://192.168.1.23for AD,ldaps://192.168.1.23:636for ADS. - Certificate Authorities: you can fill this field with a custom authority if needed for your certificate.
- Check certificate: can be checked for AD and ADS.
- Use StartTLS: should be checked if using ADS.
- Base: should be filled with your domain FQDN. Example:
dc=mydom,dc=local - DN: should be filled with a username able to connect and browse your AD. Example:
yachy@mydom.local - Password: should be filled with the user password.
- User filter: should be filled with this sAMAccountName syntax:
(sAMAccountName={{name}}) - ID attribute: should be filled with
sAMAccountName.
Group settings:
- Base: should be filled with the OU where to find groups. Example:
OU=Mygroups,OU=myorg,dc=mydom,dc=local - Filter: should be filled with the expression to filter your groups. The most basic filter can be
(objectClass=group), but you can do way more advanced LDAP expressions for filtering. - ID attribute: should be filled with
sAMAccountName. - Display name attribute: should be filled with
CN. - Group attribute: should be filled with
Member. - User attribute: should be filled with
distinguishedName.
Was this page helpful?